iOS 27: one of our alumni excels in vulnerability research
21 September 2026
Three questions to Oussama Barbar :
In what context did this vulnerability research take place?
I am involved in bug bounty programmes, which involve responsibly searching for vulnerabilities in websites, applications and systems to help organisations improve their security. Apple has a particularly significant bug bounty programme, and I had long wanted to contribute to it.
Was it simply an ‘exercise’ or research carried out under real-world conditions?
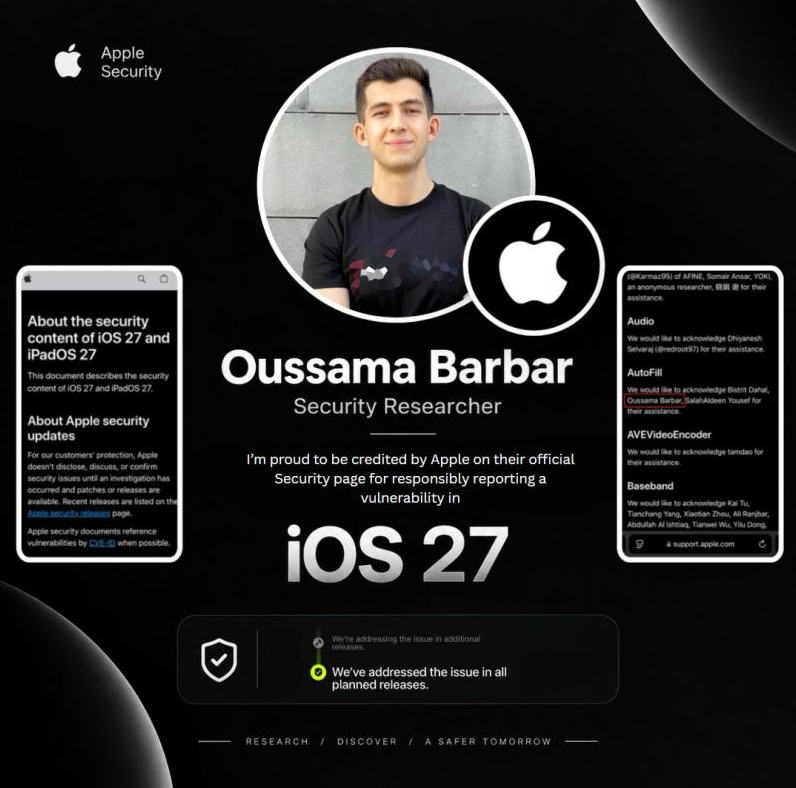
It was research carried out under real-world conditions, relating to iOS. After I reported the vulnerability to Apple, it was addressed in their Security Releases. Apple officially thanked me in the ‘AutoFill’ section.
I am very proud to see my name appear in an official Apple publication.
To what extent did your course at Télécom Paris help you?
Télécom Paris played an important role in my career path. The lectures, projects and the diversity of the areas studied in cybersecurity enabled me to develop a solid technical foundation, as well as a genuine research methodology.
Above all, the course taught me to understand how systems work, to question their behaviour and to look for problems that can be difficult to identify. This mindset is directly applicable to bug bounties.
I am therefore delighted that this experience can now be shared with the Télécom Paris community, of which I am particularly proud to be a part.
Oussama Barbar proud to be credited by Apple on their official security page for responsibly reporting vulnerability in IOS 27 (source post LinkedIn from Oussama Barbar)